AI Agent Governance Skills: What Business Professionals Must Learn Before Agents Act
By Melverick Ng | Published | Updated | 9 min read
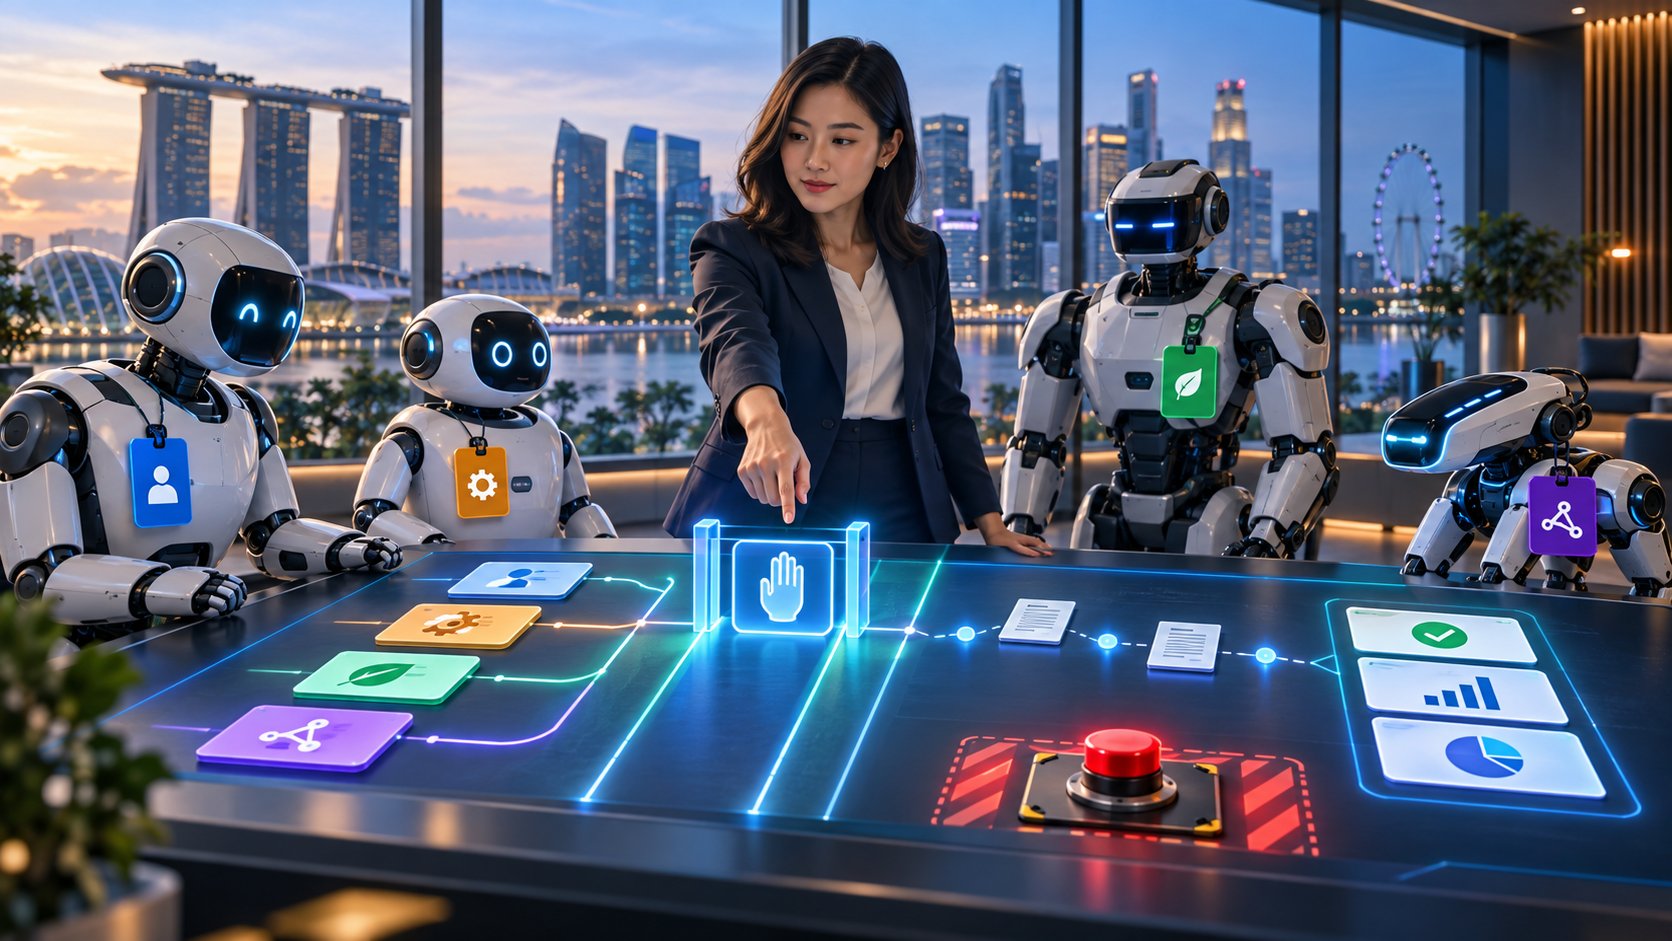
AI governance used to sound like a policy discussion for compliance teams. That changes when an AI system can call tools, update records, trigger transactions, or hand work to another agent. The risk is no longer limited to what the model says. It includes what the agent does.
Recent industry signals point in the same direction. Dataiku is framing agents as a distinct unit for inventory, monitoring, and risk management. F5 argues that governance must cover the complete chain of action. Thoughtworks has introduced a governed runtime and fleet-level control plane. Anthropic's trustworthy-agent framework emphasises human control, security, transparency, and privacy.
The operator lesson is simple: better agents do not remove the need for structure. They make good structure more valuable. Business professionals must learn to design that structure before they delegate real work.
Governance Is Becoming an Operating Skill
A policy can say that sensitive actions need approval. An operating control must identify the action, stop it at the right moment, show the reviewer the relevant evidence, record the decision, and let the workflow continue safely. That is workflow design, not paperwork.
This is why an agentic AI course in Singapore should teach more than prompts and tool features. Domain experts need to become AI architects: people who can translate business rules into permissions, checkpoints, tests, escalation paths, and evidence requirements.
1.Build an Agent Register
You cannot supervise what you cannot name. Keep a simple register for every agent: owner, purpose, systems accessed, tools allowed, data handled, current status, review date, and shutdown contact. Treat the agent as a managed worker, not an invisible feature inside a software subscription.
The register should also state what the agent must not do. A finance assistant that prepares a payment file is different from one allowed to release payment. Those boundaries need to be explicit and testable.
Next Step
Download the SME Workflow Checklist
Get the exact checklist we use to spot high-ROI automation opportunities in under 15 minutes.
2.Map the Chain of Authority
For each workflow, identify who requested the work, which agent accepted it, which tools it may use, which other agents may receive a handoff, and which human remains accountable. When an exception occurs, the escalation path should be obvious.
Do not confuse the chain of authority with the model's private reasoning. A useful audit record captures the request, trusted context, applicable rule, tool action, approval, result, and exception. That is enough to reconstruct what happened and who decided.
3.Design Least-Privilege Access
Give each agent only the data, tools, and actions needed for its current task. Start read-only where possible. Separate drafting from sending, preparing from approving, and recommending from committing a transaction.
Permissions should travel with the task, not with a broad human account copied into the agent. Time limits, spending caps, record-level access, and approved tool registries reduce the damage a mistaken or manipulated agent can cause.
4.Place Approval Gates at Consequential Moments
Human-in-the-loop does not mean a person watches every step. It means human judgment is inserted where consequences rise: before customer communication, money movement, production changes, access to sensitive data, or a final governance decision.
A good approval screen shows the proposed action, evidence, policy check, expected effect, uncertainty, and rollback option. A vague “approve?” button simply transfers confusion to the reviewer.
5.Monitor Behaviour, Quality, and Cost
Traditional monitoring asks whether a server is running. Agent monitoring asks whether the agent still performs its intended job. Track task success, correction rate, exceptions, tool use, approval frequency, latency, cost per accepted outcome, and behavioural drift.
An agent can remain online while quietly getting worse after a model, prompt, tool, or source changes. Business owners need enough telemetry to spot that drift before it becomes a customer or operational problem.
6.Test the Stop Conditions
Before live use, test missing data, conflicting instructions, unavailable tools, suspicious content, excessive cost, and actions outside scope. The agent should know when to stop, ask, retry, roll back, or escalate.
The strongest control is often not a smarter answer. It is a reliable refusal to continue when the operating conditions are unsafe or unclear.
Next Step
Check Your SkillsFuture Subsidy
See your estimated net payable fee and eligibility path in under 60 seconds.
Check My SubsidyRelated Course Module
Module: Build Your First Agentic Workflow Blueprint
Learn how to map, automate, and test one real workflow from your own business during class.
See module detailsA 30-Minute Governance Exercise
- Choose one recurring workflow where an AI agent could act across at least two systems.
- Name the business owner, agent purpose, approved inputs, tools, and prohibited actions.
- Mark one read-only starting boundary and one action that always needs human approval.
- Define the evidence that must accompany every consequential action.
- Add three failure tests and a clear stop or escalation rule for each.
- Select two quality measures and one cost-per-accepted-outcome measure.
Agent governance is not about slowing AI down. It is the operating discipline that lets digital coworkers do more real work without forcing humans to surrender control.
Sources
- Dataiku: Every enterprise is building agents. Almost none can account for them.
- TNGlobal: F5 on governing AI agents at runtime
- Thoughtworks: Agent/works governed runtime and control plane
- Anthropic: Trustworthy agents in practice
About the Trainer
Melverick Ng is Founder of Nexius Labs and Master Trainer at Nexius Academy. He has trained business teams and non-technical professionals to design practical AI workflows for sales, operations, and customer support.
Talk to a Course Advisor